[ACSA Training #36] Routing Protocols
Before learning about routing protocols, we AS(Autonomous System)It is necessary to understand.
An Autonomous System can be thought of as a collection of routers under a management domain.
In other words, an ISP (Internet Service Provider) owns its own internal network. And the ISP has the autonomy to manage even the routers within that network. This is called an Autonomous System (AS).
Additionally, each company also manages its own network. This also becomes an AS (Autonomous System).
To route packets within the AS, each company Interior Gateway Protocol (IGP)Use .
IGP is a simple routing protocol that runs inside an AS.
Examples of IGPs include Routing Information Protocol (RIP), Intermediate System-Intermediate System (IS-IS), and Open Shortest Path First (OSPF).
Each company will choose and use the IGP that is right for them.
Each business connects to the Internet through an ISP line, and each ISP has its own unique AS number.
Enterprises want to route between their AS and the AS of their ISP. In order to achieve this inter-AS routing in an enterprise environment, Exterior Gateway Protocol (EGP)This is required.
The only EGP currently in use is Border Gateway Protocol (BGP).
Let's compare IGP and EGP using the picture below as an example.
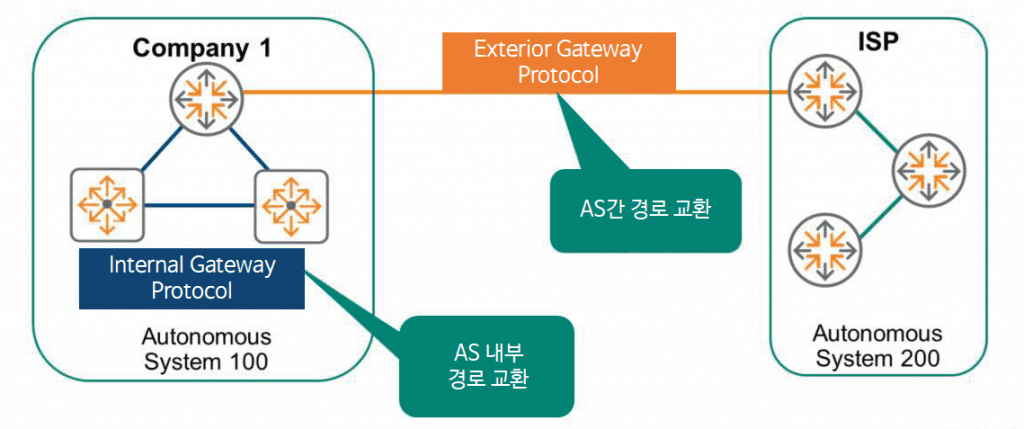
In the figure, the ISP has three router devices in a system called AS 200.
Additionally, Company 1 has an AS called AS 100 and has routers and multilayer switches.
In Company 1, network information is exchanged between multilayer switches and routers to discover all paths within the AS and select the optimal path to reach each network. This is the Interior Gateway Protocol (IGP).
And Company 1 needs to communicate with the outside world. For Internet communication, we need to check with our ISP and the outgoing route.
They exchange route information with each other through AS numbers. This is the Exterior Gateway Protocol (EGP).
Distance Vector Routing Protocol
The method initially designed to exchange IP information was to use the Distance Vector algorithm.
Each router announces its distance and direction (or vector) from each network, and packets travel to reach that network. Distance is measured in the number of "hops.".
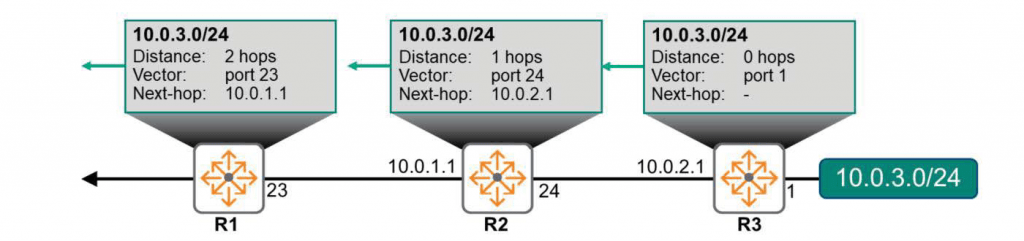
In the example in the figure above, how many hops does the R3 device need to reach the network 10.0.3.0/24?
The answer is... 0. This is because the network is directly connected to the R3 device.
So what is the vector or direction for R3 to send the packet to 10.0.3.0/24?
as soon as Port 1(port #1).
That is, in order to get from R3 to a host in the destination network 10.0.3.0/24, the packet must be forwarded through local port 1.
Here, if a protocol such as RIP or RIPv2 is used, R3 informs R2 of the distance and vector information.
R2 receives this information and understands, "The destination network 10.0.3.0/24 must go through R3, and R3 is 0 hops away from that network. So I'm 1 hop away from the destination network." Additionally, it knows that to reach the destination network, it must forward packets from local port 24 to 10.0.2.1.
Here again R2 informs R1 of its information (distance and vector).
R1 realizes that to reach the destination network 10.0.3.0/24, it must go through R2, which is one hop away from the destination, and thus two hops away from itself (R1). It also realizes that to reach the destination network, which is two hops away, R1 must forward packets from local port 24 to 10.0.1.1.
Distance Vector routers are unaware of the overall network topology. Each router is only aware of its own directly connected routing peers. This simplifies operations, but also imposes the following limitations:.
- Slow convergence: When a failure occurs, it can take a long time for the new routing path to be adjusted, depending on the network size, complexity, and architecture.
- Limited scalability: Each router cannot be more than 15 hops away from any other router.
※ Even relatively simple architectures can have dozens or hundreds of routers.
Routing protocols that use distance vectors include Routing Information Protocol (RIP), RIP version 2 (RIPv2), and RIP Next Generation (RIPng). RIP and RIPv2 do not support security features to protect messages exchanged between routing devices.
Therefore, due to limited scalability, performance and security reasons ArubaOS-CX does not support the Distance Vector protocol.
Instead, it supports a more robust Link State routing protocol.
Link State Routing Protocol
Link State routing protocols address the limitations and shortcomings of Distance Vector protocols.
Routers running link-state protocols have information about the entire network topology. This allows them to independently compute routing tables using a more sophisticated Dijkstra algorithm, allowing them to select the most optimal path for every network destination.
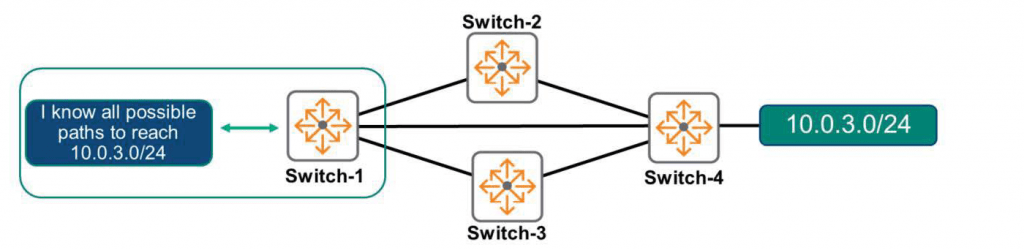
Using Link State protocol...
There is OSPFv2 (Open Shortest Path First version 2) used in IPv4, OSPFv3 used in IPv6, and IS-IS (Intermediate System-Intermediate System).
Since OSPF is actually used more than IS-IS, I will focus on OSPF in the next post.
Link State protocols offer faster convergence times than Distance Vector protocols and also offer advantages in scalability.
Just a few years ago, protocols like OSPF had the disadvantage of consuming more CPU, memory, and bandwidth than protocols like RIP. However, routers have evolved over the years to offer more features and have become capable of designing more efficient network architectures.
So these concerns have been greatly reduced these days.
ArubaOS-CX multilayer switches are designed to meet today's network requirements.
“You can check this information using the ”show capacity ospfv2” command.
Switch-6300# show capacities ospfv2
System Capacities: Filter OSPFv2 Capacities Name Value -------------------------------------------------------------------------- Maximum number of OSPFv2 areas configurable in the system 128 Maximum number of OSPFv2 interfaces configurable in the system 128 Maximum number of OSPFv2 interfaces per area in the system 128 Maximum number of OSPFv2 neighbors allowed across all VRFs 128 Maximum number of OSPFv2 processes supported across each VRF 1 Maximum number of routes in OSPFv2 supported across all VRFs 64000
Today, following up on the last post, we learned a little more about routing.
In the last post, we learned about static routing protocols, and today we learned about dynamic routing protocols.
In practice, OSPF and BGP protocols are most commonly used in the field.
So, the next post will focus on OSPF.