Global Substation Security Scan Results: "Breached in 30 Minutes?"“
Today, I'd like to introduce you to a very "heart-pounding" report that is directly related not only to the security industry but also to our daily lives.
Austrian energy security specialist OMICRON's survey of over 100 power plants and substations around the world revealed:But the content is quite shocking.
“As soon as we installed the IDS (Intrusion Detection System), critical vulnerabilities started pouring out in just 30 minutes.”
What exactly was the problem, and how should we prepare?
Unlock OT security with HPE Aruba Networking solutions. Start now!
Omicron warns of the top 5 OT security risks.
The security reality on the ground was far more serious than previously thought. The report identified five key risks:.
- Museum-grade vulnerabilities neglected: Patch came out in 2015
CVE-2015-5374The same old vulnerabilities are still active(?). - The 'Ghosts' of the Factory (Shadow OT): IP cameras, printers, etc. that are not listed in the management ledger are connected to the core control network without authorization.
- Flat Network: There are countless examples of logically indistinguishable connections, from office IT networks to remote substation controllers.
- Undocumented external access: At just one substation, over 50 external TCP/IP connections of unknown origin were discovered. The back door was wide open.
- Barriers between departments (Silos): Lack of communication between IT and OT teams makes security responsibility unclear, leading to missed golden time for response.
So what's the solution? OT Security Architecture Based on HPE Networking
To end this 'security chaos party', we are focusing on everything from visibility to remote access. three-dimensional defense systemWe need to build it.
1️⃣ “If you can’t see it, you can’t stop it” – The magic of ClearPass’s ‘visibility’
The most shocking thing in the article was 'Ghost Devices'.
IP cameras and printers that even the person in charge doesn't know about are connected to the substation core network.
Problem: Unlike general PCs, the OT environment is mostly comprised of PLCs, IEDs, and RTU equipment that cannot be installed with antivirus software.
Since we don't know what's what, we leave everything open, which is called 'security neglect'.
Solution: ClearPass or Central's Client InsightYou need to invest.
- AI-based profiling: It doesn't simply look at the MAC address. It analyzes the traffic patterns, response speeds, and protocol characteristics of the device to accurately identify it, such as, "Is this a Siemens PLC?" or "Huh? That's a Xiaomi camera?".
- Enforcement: When an unauthorized "ghost" is detected, the switch port is immediately shut down or moved to a quarantine VLAN, eliminating the need for a human to manually search for it.
2️⃣ “Put Barricades on the Highway” – Network Segmentation with SRX
The article warned of the dangers of a "flat network" that runs like a highway from IT offices to core substation equipment.
Problem: If an office PC is infected with ransomware, the substation control system can be paralyzed immediately.
Solution: HPE Networking SRX (Juniper) It's the series' turn to take the mound.
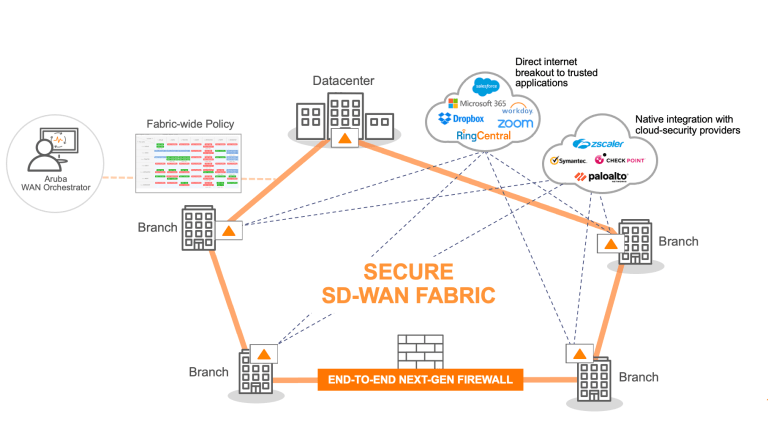
- Deep Packet Inspection (DPI) for OT: Typical firewalls do not understand OT protocols such as Modbus or IEC 61850.
However, SRX can look deeper and block this command to determine whether it is a 'simple monitoring' or a 'system shutdown' command. - L7 Microsegmentation: Establish a strong 'checkpoint' between IT and OT networks, controlling only authorized traffic to pass through at authorized times.
3️⃣ “Backdoor crackdown is urgent” – Secure remote access through SASE/SSE
Only at one substation More than 50 external TCP/IP connections of unknown originCan you believe this was discovered?
The 'back door' left open for maintenance became an entrance for attackers.
Problem: Once a traditional VPN is compromised, the entire network is exposed. Furthermore, real-time monitoring of external activities is difficult.
Solution: HPE Aruba Networking SSE (ZTNA)Apply .
- Zero Trust Access: “The principle is ”trust no one.”.
When an external engineer connects, the entire network is not opened. Only that specific PLC that needs to be fixedGrants access only to . - Stealth Mode (Dark Cloud): We hide our substation infrastructure from the internet.
Even if an attacker scans our IP, our device will not respond, so they cannot even attempt an attack.
✅ [Self-Diagnosis] Is our workplace OT security okay as it is?
Check it out now!. “If there is even one ”No (N)”, it is a red flag!
| Diagnostic items | Result (Y/N) |
| 1. Do you have a real-time list of all devices (PLCs, IEDs, etc.) connected to the network? | |
| 2. Is it immediately blocked when an unauthorized device (camera, personal laptop) is connected? | |
| 3. Do you know the firmware version and known vulnerability (CVE) information of your field equipment? | |
| 4. Are the IT network and OT network completely separated logically and physically? | |
| 5. When connecting to an external company, is access restricted to only ‘specific devices’ rather than the entire network? | |
| 6. Is two-factor authentication (MFA) required for all remote access? |
Conclusion: Security starts with the mindset that it's "my job"!
As the report points out, what's scarier than technology is the mindset that draws the line and says, "This is not my responsibility.".
We can't afford to let vulnerabilities discovered in 2015 still be around in 2026!
Protecting our nation's critical infrastructure is easier than you think with HPE Aruba Networking.