

The 'PHP2Shell' Crisis That Shook the Foundation of the Internet: How Does HPE Networking SRX Block It?
A massive issue has broken out that has kept the global security industry and IT infrastructure operators awake at night. It is... ‘'PHP2Shell(CVE-2026-109618, CVE-2026-109619)'’ It is a situation.
As the name suggests—reminiscent of 'Log4Shell,' which once terrified the world—this vulnerability is also being evaluated as unprecedented in terms of its impact and level of threat.
How the recent PHP crisis unfolded and why it is so fatal, and HPE Networking SRX FirewallWe will summarize how you can immediately defend against this threat at the network level through this.
1. The 'PHP2Shell' Incident: How on Earth Did It Happen and Why Is There Such an Uproar?
The incident began on October 21st.
The PHP development team has released urgent security patches to address two critical remote code execution (RCE) vulnerabilities (CVE-2026-109618, CVE-2026-109619).I did, but the problem is Related information was leaked in advance the day before (October 20), even before the official patch was released.The point is that it became.
As a result, within just a few hours of the patch's release, active exploits and proof-of-concept (PoC) code flooded the world indiscriminately.
There are three main reasons why the security industry has called this incident 'PHP2Shell' and issued the highest level of alert.
- Flaws in the 'PHP engine itself' supporting the 75% of the web ecosystem: It is not merely a matter of a single website or plugin being poorly made. It involves WordPress, Drupal, Laravel, and others that power the majority of the global web. Memory handling defects in the PHP core engine (Runtime) itselfNot only externally exposed websites, but also PHP embedded in internal corporate management consoles and third-party solutions are all within the attack range.
- A single request that doesn't even require a login (Unauthenticated RCE): The risk score reaches 9.8 (Critical) on the CVSS scale. Hackers do not need separate login privileges or complex bypass processes. By simply sending cleverly manipulated data on a standard HTTP request that the server processes by default, a 'Web Shell' that seizes control of the server is immediately executed as the PHP engine's memory areas (such as Out-of-Bounds) become corrupted.
- Neutralization of Application Security: What is even more critical is the timing of the attack. The vulnerability strikes at the lowest level, the PHP engine, before the web application's business logic or security plugins can even finish executing. In other words, the server can be breached before any defense code embedded within the application has a chance to react.
2. HPE Threat Labs' Immediate Response: Urgent Deployment of SRX Firewall IDP Signatures
As such, indiscriminate scanning and attacks began immediately after the patch was released, but for companies, it is practically impossible to update the PHP versions of all their numerous web servers and legacy systems overnight. To put out the immediate fire without service interruption or compatibility testing, Cutting off malicious traffic at the network perimeter before it reaches the web serverThis is the only answer.
In response to this, HPE Threat Labsimmediately after the incident occurred October 22, 2026, Updated to detect exploit attempts matching known PHP2Shell attack patterns and immediately block corresponding traffic in inline enforcement environments. IDP (Intrusion Detection and Prevention) Signatures for SRX FirewallWe have urgently released it.
🛡️ PHP2Shell IDP Signature Summary
- Signature Name:
HTTP:PHP:PHP2SHELL-OOB - Severity: Critical
- Target CVE: CVE-2026-109618, CVE-2026-109619 (CVSS 9.2)
- Release Date: October 22, 2026
Latest IDP Signature (HTTP:PHP:PHP2SHELL-OOBThe SRX firewall with applied ) performs real-time, thorough inspection of all traffic destined for backend PHP applications along the traffic path, and blocks attack packets at the network level according to policy as soon as abnormal patterns matching PHP2Shell exploit activity are detected.
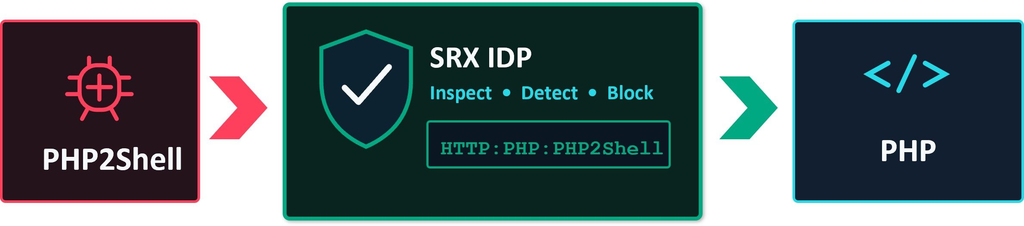
IDP protection in firewalls buys time until patches are applied and is a key means of implementing Defense-in-Depth, but It does not completely replace the fundamental software patch..
You must resolve the immediate crisis using IDP signatures and proceed with PHP runtime updates sequentially. (※ Be sure to check whether SSL Inspection is configured to prevent attacks via encrypted HTTPS traffic.)
3. SRX Firewall Implementation and Response Guide (Practical Checklist)
If you are a security and network manager operating the equipment in the field, you must immediately take the following measures to establish a secure defense line.
① IDP Signature Update and Verification
Quickly download and apply the latest IDP signature package on the SRX machine. You can monitor the package version and update progress in real time using the command below from the machine CLI.
Check # IDP signature package version
show security idp security-package-version

Check # IDP Signature Download Progress and Status
request security idp security-package download status
Please make sure to run the command to check if the latest packages from October 22, 2026 or later have been successfully applied.
② Enable Inline Enforcement Policy
Identified HTTP:PHP:PHP2SHELL-OOB You must check whether the signature remains in a simple detection and logging (Alert/Ignore) state, and ensure that actual malicious packets can be intercepted Drop/Block PolicyYou need to check if it is applied inline.
4. Patching and infrastructure upgrades recommended for a fundamental solution
Preemptive defense through the firewall's IDP/IPS performs the role of powerful virtual patching and layered defense that protects internal assets from external attacks and buys time for patching, but, It cannot replace a fundamental solution that addresses vulnerabilities in the software itself.
You must carry out the following fundamental remediation work in parallel while maintaining the temporary defense line.
- Backend PHP Upgrade: You must immediately identify the runtime version of PHP-based applications running in-house and update them to the latest version or higher that includes patches to address the security vulnerabilities listed below.
👉 Recommended PHP Patch Version: 8.5.12, 8.4.27, 8.3.36, 8.2.35 or later - Ensuring the security of the SRX firewall itself: Many network and security devices use PHP in their built-in web servers, so they are often vulnerable to threats.
However, in the case of the HPE SRX series, Starting with the Junos OS 25.2 release, PHP is not used at all due to the architecture (Does not use PHP) It is completely safe from that issue.
If you are using an older release version below 25.2, the latest version is necessary to eliminate potential risks to the firewall itself. Upgrade to version 25.2 or higherI strongly recommend doing this.
Checklist to check right now
The PHP2Shell incident, in which the attack began before the patch with a time difference of just one day, involved the rapid reflection of threat intelligence at the network level and Security internalizationIt reminded me once again how important it is.
If you are currently operating an HPE Networking SRX firewall, please check the following three things right now.
- IDP Signature DB Update: Whether the latest IDP security package distributed since October 22 has been downloaded, and
HTTP:PHP:PHP2SHELL-OOBPlease check if the signature is included correctly.- Inline Enforcement Settings Check: Check the policy to ensure that the signature is configured with an inline blocking action to cut off actual malicious traffic, rather than stopping at simple detection and logging (Alert).
- Maintain continuous signature automatic updates: As HPE Threat Labs continues to update signatures based on additional data, please keep update cycles short and strengthen monitoring for the time being.
- PHP Version Upgrade: Do not blindly trust the IDP function; update to a secure version by patching the actual backend PHP server.