Core Features of Zero Trust Network Security
October is Cybersecurity Awareness Month, focusing on protecting individuals and organizations from cybercrime.
One way organizations can address cybersecurity challenges is by adopting “zero trust network security.”.
However, fully implementing a zero-trust network security strategy can lead to problems.
Zero Trust focuses on providing least-privileged access to resources based on role and continuous monitoring, but role-based access control is often fragmented or poorly enforced across multiple, disintegrated platforms.
5 Essential Capabilities for Zero Trust Network Security
The Zero Trust network security framework is based on five core capabilities:.
- Visibility – Identify and profile users and devices on your networkdo.
- Authentication and Authorization – Define roles and assign them to users and devices Assign detailed role-based policiesdo.
- Role-based access control – for resources across the network Automatically enforces least privilege access controldo.
- Conditional monitoring – Deliver real-time information bidirectionally within your security technology stack.
- Implementation and Response – Automatically respond to situational threat signals by limiting or revoking access.
Aruba is Central NetConductor, a cloud-native network automation and orchestration solution, enabling organizations to easily adopt these capabilities.
Central NetConductor, part of Aruba Central, includes all the tools you need to build, configure, and operate a network that supports a Zero Trust network security strategy.
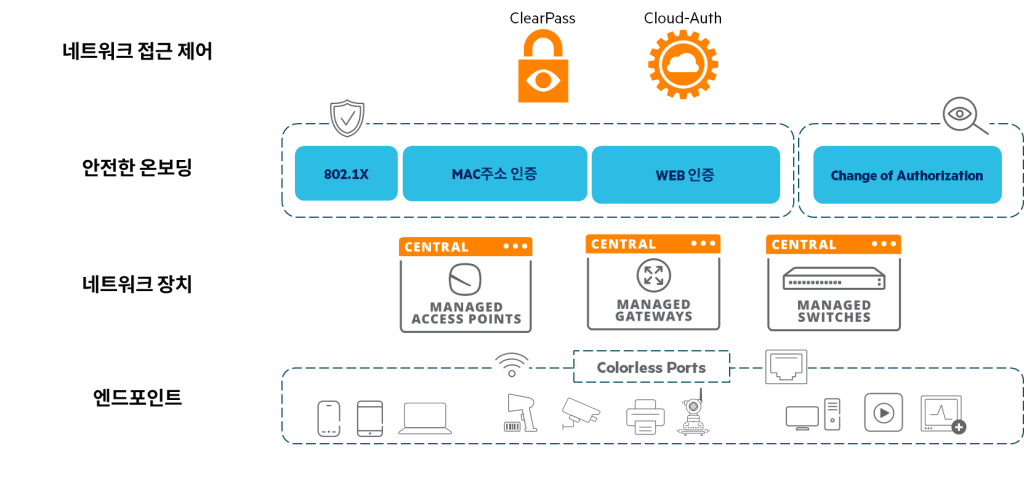
Central NetConductorYou can benefit by supporting a Zero Trust network security strategy.
Okay, so the organization Central NetConductorLet's see how to implement zero trust network security using .
Step 1. Understand the flow of network traffic
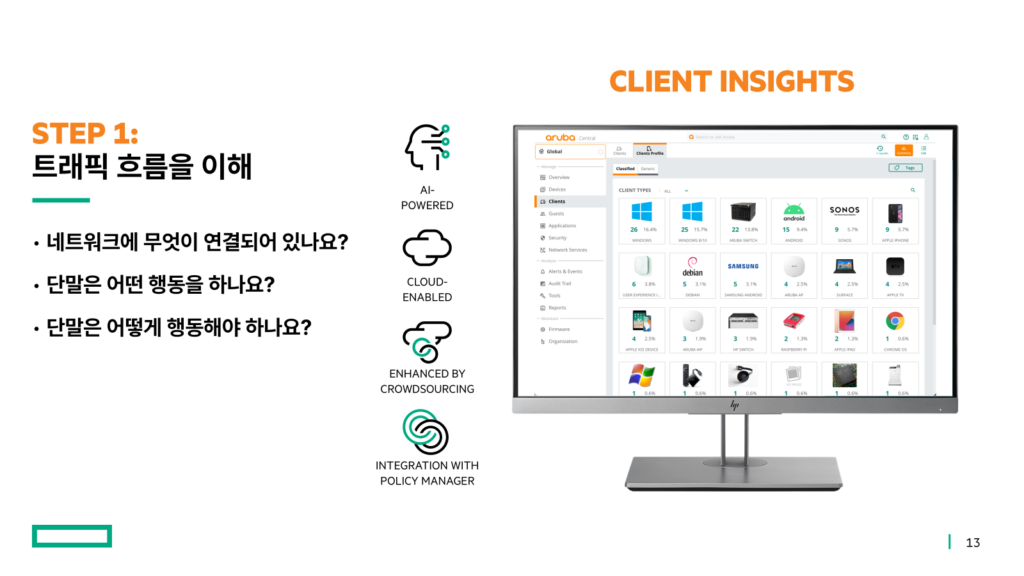
The first step is to determine how endpoints are mapped to roles and define a minimum set of access rules based on what users or endpoints are expected to do on the network and the normal behavior of that user/device.
Client InsightsIt provides visibility into traffic flows as well as endpoint types on the network.
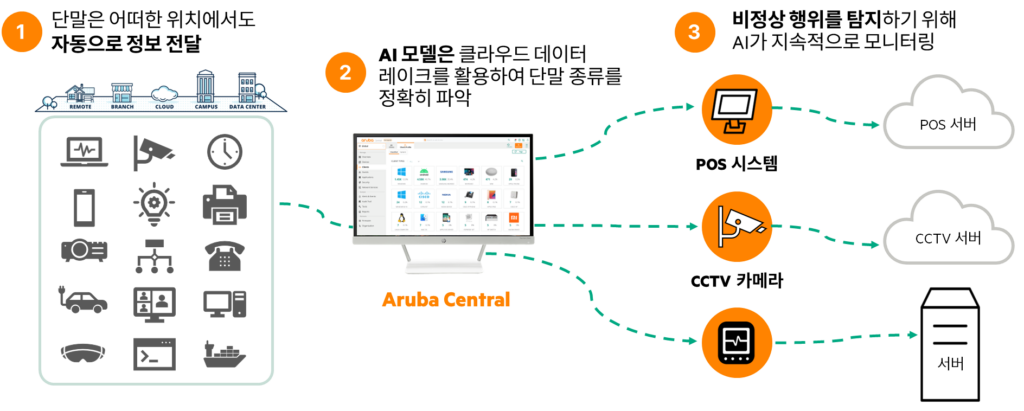
Based on information collected from data on Aruba network devices and transmitted to Aruba Central, Client Insights uses tools like machine learning to easily classify and sort different device types, such as printers, cameras, and HVAC systems.
Step 2. Authenticate your device on the network
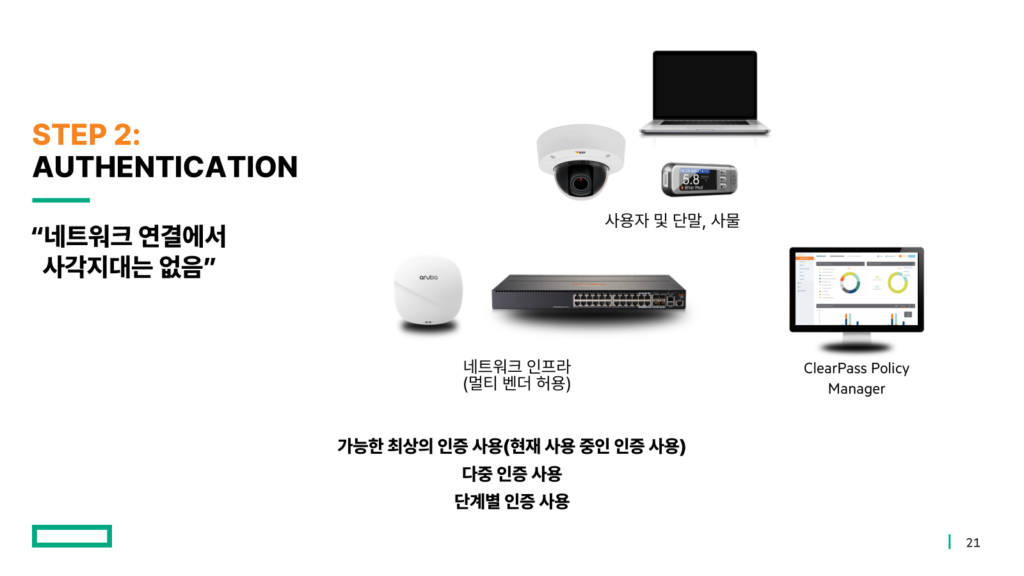
After identification, endpoints must be authenticated. It's crucial to verify that endpoints are as trustworthy as they claim to be. It's recommended to first authenticate each device using the strongest available method, then assess compliance with corporate endpoint policies before assigning roles.
For example, an employee laptop can first authenticate using the 802.1X protocol to ensure that the endpoint is actually a laptop.
We check for the presence of an asset management tool within the company and verify proper mapping between usernames, passwords, and terminals. Only after these checks are confirmed is the laptop assigned the "Employee" role.
Authenticating IoT devices can be a bit more challenging. Organizations have traditionally relied on MAC address-based authentication, but if IoT device manufacturers map multiple types of IoT devices to the same MAC address, the results can be inconsistent.
Client Insights learns traffic flows and patterns, not just MAC addresses, to more accurately identify endpoints, enabling IT teams to more confidently assign roles to users and devices.
Step 3. Apply trust
NetConductor provides organizations with the flexibility to use a centrally managed, distributed Trust Enforcement Model.
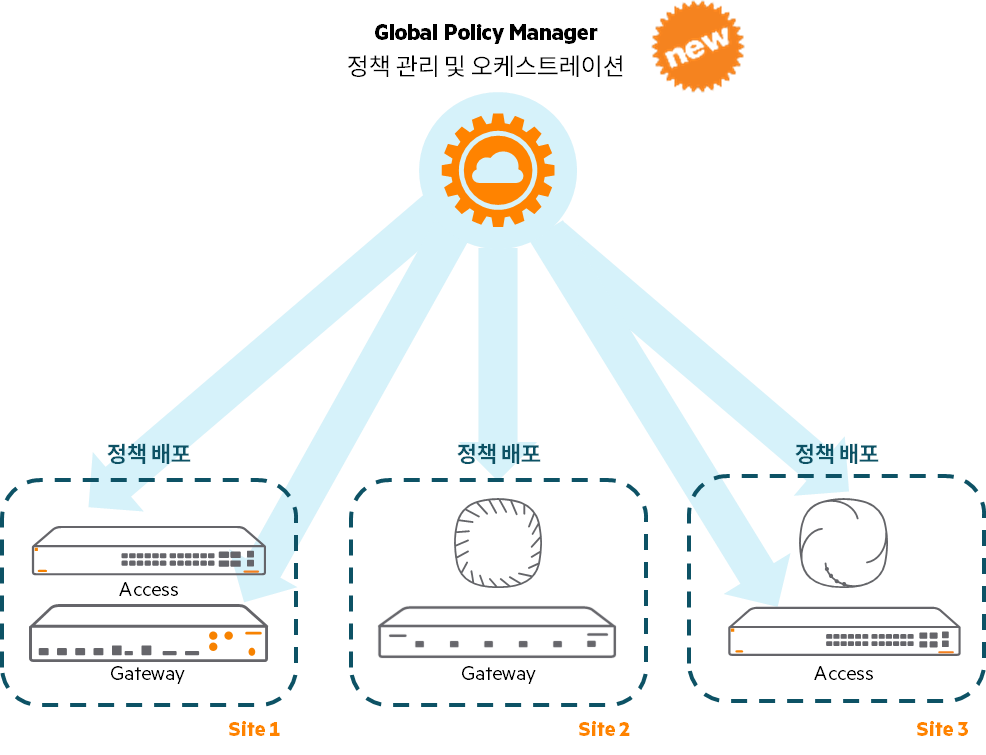
Dynamic SegmentationThrough this, IT can consistently enforce role-based access control rules applied to devices like printers anywhere on the network, providing true Zero Trust network security where network endpoint traffic only goes where it should go.
Central NetConductor also reduces network complexity, making it easier to adopt a Zero Trust security model. There's no need to organize VLANs or routing tables in Excel spreadsheets or manually configure ACLs every time.
At deployment time, the Fabric Wizard simplifies overlay creation using an intuitive GUI, greatly streamlining the process of defining virtual components and generating configuration instructions to push them down to the infrastructure.
Once deployed, these access control policies automatically propagate across your network within minutes, continuously reflecting business-specific workflows and associated role-based access without any manual intervention or updates.
Step 4 & Step 5. Share context and respond to threats.
We share context with each other across the security ecosystem. This allows us to leverage all available data to make dynamic access decisions.
Aruba uses ClearPass, the industry-leading network access control solution, to ensure every endpoint on your network has the desired level of security, in collaboration with over 150 security partnerships (part of the Aruba 360 Security Exchange program). ClearPass can restrict access or revoke authorization for any device that fails to meet security requirements or attempts to perform actions inappropriate for its role.
For example, a printer on your network might be communicating with a restricted country or attempting an attack based on a pattern found in the IDS/IPS signatures of a security appliance with Aruba Echo Partnership.
ClearPass can then receive this information and communicate with network devices to move them from their printer role to an isolation space, apply a different set of enforcement policies to that endpoint, and ultimately ensure that no malicious devices are present on the network.
Aruba offers several security devices to help organizations keep their networks secure.
ClearPass provides role assignment and role-based policies, and Aruba's wired and wireless network devices support the Dynamic Segmentation solution, which enables consistent role-based network segmentation and policies to be applied regardless of network type.
Going further, Aruba Central offers a feature called Central NetConductor, which helps provide consistent policies across global sites and allows for easy policy orchestration and provisioning.
Aruba's solutions enable a zero-trust security model that enables secure access to resources through authentication, authorization, and encryption, regardless of the connected network.